RuboCop
Ruby static code analyzer and formatter
Discover. Evaluate. Test.
Software composition analysis for known vulnerable dependencies
OWASP Dependency-Check is a software composition analysis (SCA) tool that detects publicly disclosed vulnerabilities in a project’s dependencies. It determines whether a Common Platform Enumeration (CPE) identifier exists for each dependency and, if so, generates a report linking to the associated CVE entries.
Vulnerability data comes from the NIST National Vulnerability Database through the NVD API. Dependency-Check 11.0.0 and later require Java 11. Its architecture can be extended, as described in the project wiki.
Dependency-Check is an OWASP project distributed under the Apache License 2.0. Its repository has moved to the dependency-check organisation on GitHub, where it is actively maintained; version 13.0.0 was released in August 2026.
There are no reviews yet.
Ruby static code analyzer and formatter
Static analysis of Java and JSP source code (end of life)
Static analysis tool checking Java source code against coding standards
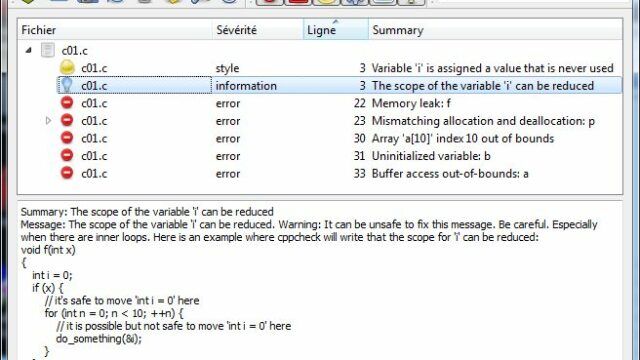
Static analysis tool for C and C++ code
Finds common security issues in Python code
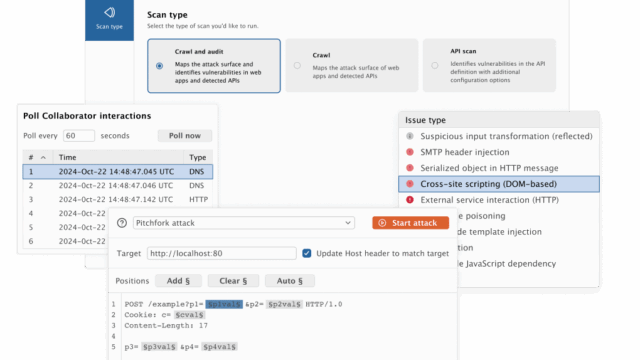
Toolkit for web application security testing