
Insure++
Runtime memory error detection for C and C++
Discover. Evaluate. Test.
Library of reusable fuzzer components in Rust
LibAFL is a collection of reusable pieces of fuzzers, written in Rust. It gives many of the benefits of an off-the-shelf fuzzer while being completely customisable, so that custom fuzzers can be assembled and extended. It is developed by the AFL++ team.
LibAFL does as much as possible at compile time to keep runtime overhead low, and scales almost linearly over cores, and over several machines through TCP, with its Low Level Message Passing mechanism. Every part can be replaced, for example to use an AST-based input for structured fuzzing. It runs on Windows, macOS, iOS, Linux and Android, and can be built without the standard library to target embedded devices or hypervisors. Binary-only modes such as Frida mode and source-based instrumentation passes are supported.
LibAFL is free and open source under the Apache 2.0 or MIT licence.
There are no reviews yet.
Runtime memory error detection for C and C++
Coverage-guided semantic fuzzing for Java
Coverage-guided, in-process fuzzer for the JVM
Stateful REST API fuzzing from OpenAPI specifications
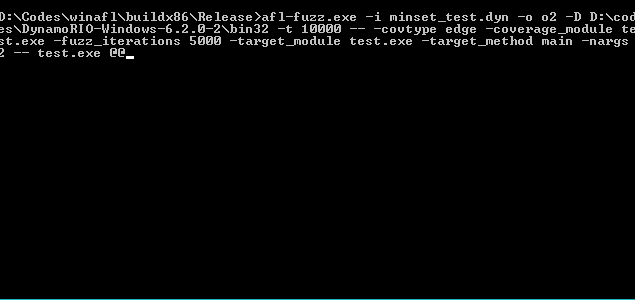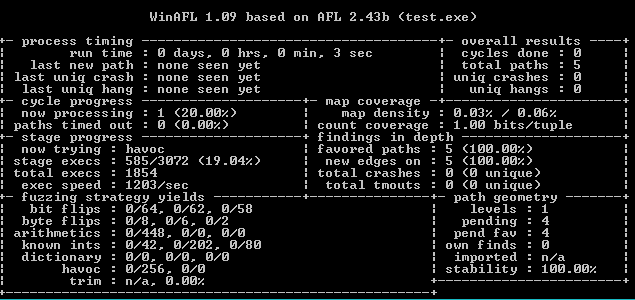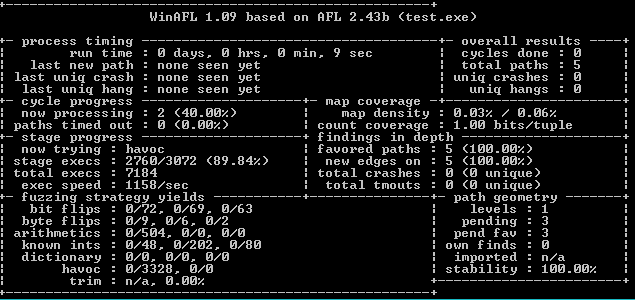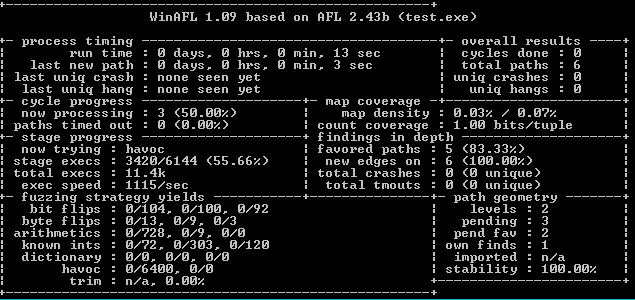
Fork of AFL for fuzzing Windows binaries
Fills web forms with pseudorandom data