Fortify
Application security testing: static analysis, dynamic testing and SCA
Discover. Evaluate. Test.
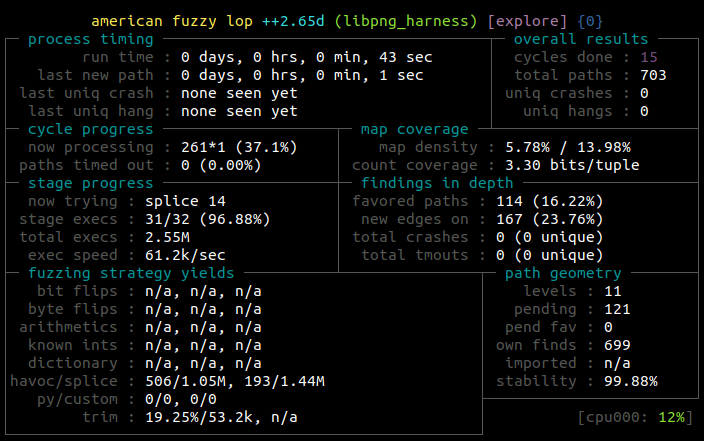
Coverage-guided fuzzing framework, successor of AFL
AFL++ is a fuzzing framework derived from American Fuzzy Lop (AFL) by Michał Zalewski. It was created to bring together the improvements developed over the years for fuzzers of the AFL family that were never merged into AFL, which has not been updated since November 2017.
The framework includes afl-fuzz, a fuzzer with many mutators and configurations; source code instrumentation modules (LLVM mode, afl-as and a GCC plugin); binary instrumentation modules (QEMU, Unicorn and QBDI modes); and utilities for minimising test cases and corpora. It is used to find crashes and security vulnerabilities by feeding programs with mutated inputs.
AFL++ is open source and actively developed on GitHub; version 5.03c was released in September 2026.
There are no reviews yet.
Application security testing: static analysis, dynamic testing and SCA
Security platform for code, dependencies, containers and cloud configurations
Property-based API testing from OpenAPI and GraphQL schemas
Test case generator for robustness testing (fuzzer)
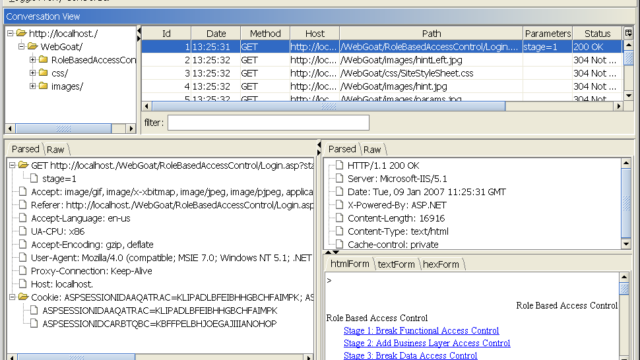
Framework for analysing HTTP(S) application traffic

Unit and integration test tool of the LDRA tool suite