
Ballista OS Robustness Test Suite
POSIX function robustness test suite from the Ballista project (unsupported)
Discover. Evaluate. Test.
Coverage-guided fuzzer for JavaScript engines
Fuzzilli is a coverage-guided fuzzer for dynamic language interpreters, based on a custom intermediate language, FuzzIL, which can be mutated and translated to JavaScript. It is aimed at finding bugs in JavaScript engines.
To use it, the source code of one of the supported engines, such as V8, SpiderMonkey or JavaScriptCore, is patched and compiled with coverage instrumentation, then Fuzzilli generates and mutates programs in FuzzIL and runs them in the engine. Working on an intermediate language keeps the generated programs syntactically and semantically meaningful. Several instances can be connected to fuzz in a distributed way.
Fuzzilli was started at Google Project Zero, is written in Swift, and is free and open source under the Apache 2.0 licence.
There are no reviews yet.
POSIX function robustness test suite from the Ballista project (unsupported)
Simulates common network problems for testing distributed systems
Property-based API testing from OpenAPI and GraphQL schemas
In-process, coverage-guided, evolutionary fuzzing engine
Coverage-guided, in-process fuzzer for Node.js
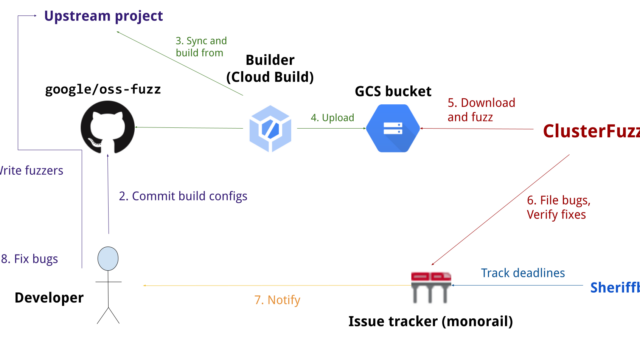
Continuous fuzzing service for open source software