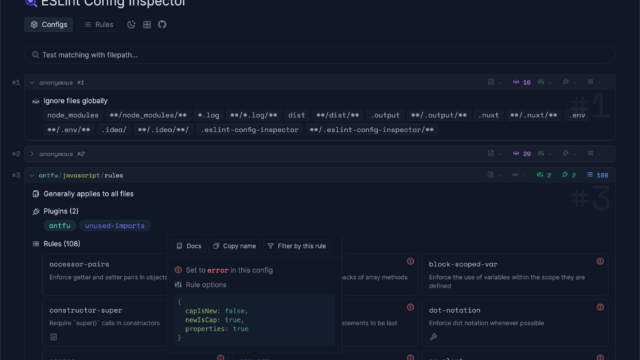
ESLint
Pluggable linter for JavaScript and JSX
Discover. Evaluate. Test.
Vulnerability scanner for container images, file systems and SBOMs
Grype is a vulnerability scanner for container images, file systems and software bills of materials (SBOMs). It supports the major OS package ecosystems, such as Alpine, Debian, Ubuntu, RHEL, Oracle Linux and Amazon Linux, as well as language-specific packages for Ruby, Java, JavaScript, Python, .NET, Go, PHP, Rust and others.
Grype handles Docker, OCI and Singularity image formats. Results can be prioritised with EPSS, the Known Exploited Vulnerabilities (KEV) catalogue and risk scoring, and filtered or augmented with OpenVEX documents.
Grype is developed by Anchore, written in Go and distributed under the Apache License 2.0; it is actively maintained on GitHub.
There are no reviews yet.
Pluggable linter for JavaScript and JSX
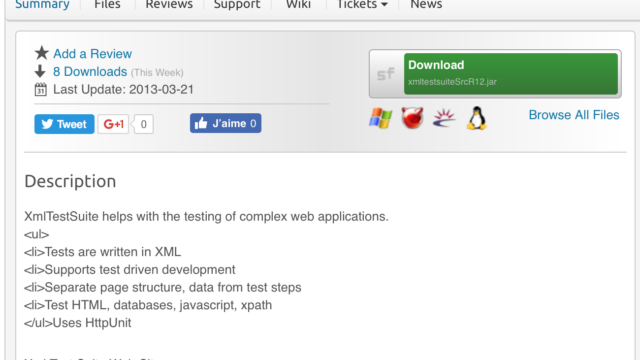
XML-based testing of web applications
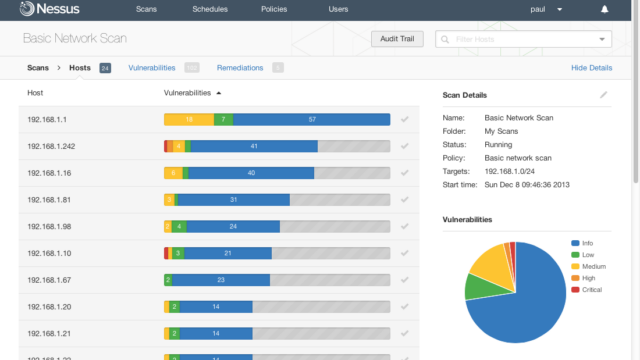
Vulnerability assessment scanner
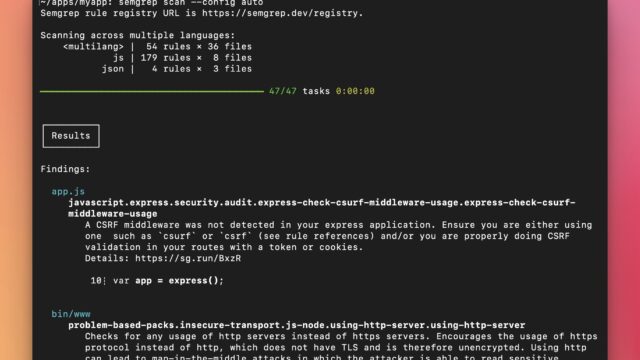
Fast static analysis with rules that look like code
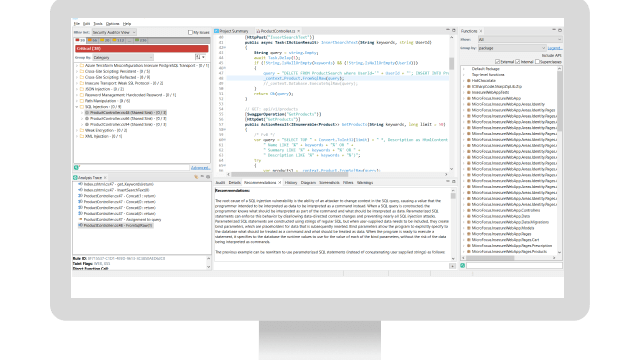
Application security testing: static analysis, dynamic testing and SCA
Ruby static code analyzer and formatter