Comcast
Simulates common network problems for testing distributed systems
Discover. Evaluate. Test.
Dynamic code and API security testing with fuzzing
Mayhem is a dynamic application security testing platform built on advanced fuzzing and integrated symbolic execution. It tests compiled code and APIs in the development pipeline and creates a proof of vulnerability for each defect it reports.
Code security testing fuzzes applications and libraries with intelligent triage, API testing stress-tests APIs against the OWASP Top 10 API weaknesses with stateful positive and negative tests, and a dynamic SBOM uses reachability analysis to show which components are actually on the attack surface. Results are presented in one dashboard and as SARIF reports, with integrations for GitHub, GitLab, Jenkins, CircleCI, Azure DevOps, Jira and Slack.
Mayhem originated in ForAllSecure, and Mayhem Security has been acquired by Bugcrowd. It is a commercial product.
There are no reviews yet.
Simulates common network problems for testing distributed systems

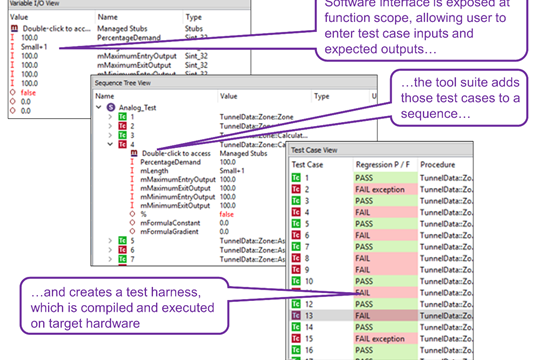
Unit and integration test tool of the LDRA tool suite
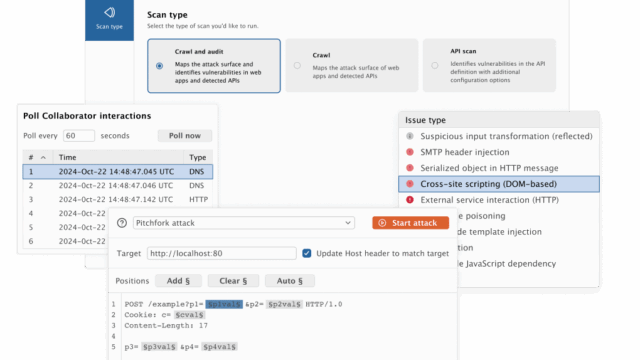
Toolkit for web application security testing
LLM vulnerability scanner
Java HTTP/HTTPS proxy for web application security testing
Test case generator for robustness testing (fuzzer)