FLUCTUAT
Static analyzer for numerical precision in C and Ada programs
Discover. Evaluate. Test.
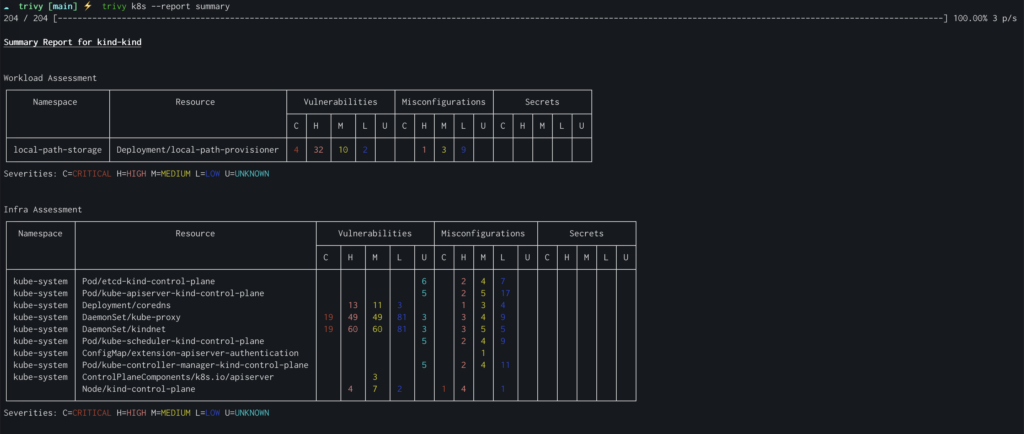
Scanner for vulnerabilities, misconfigurations and secrets
Trivy is a comprehensive security scanner by Aqua Security. It looks for known vulnerabilities (CVE) in OS packages and software dependencies, misconfigurations in infrastructure as code, sensitive information and secrets, and can generate a software bill of materials (SBOM).
Scan targets include container images, file systems, code repositories, binary artifacts and Kubernetes clusters. Trivy supports most popular programming languages, operating systems and platforms, and is available through common distribution channels such as binaries, package managers and container images.
Trivy is written in Go, distributed under the Apache License 2.0 and actively developed on GitHub; version 0.76.0 was released in October 2026.
There are no reviews yet.
Static analyzer for numerical precision in C and Ada programs
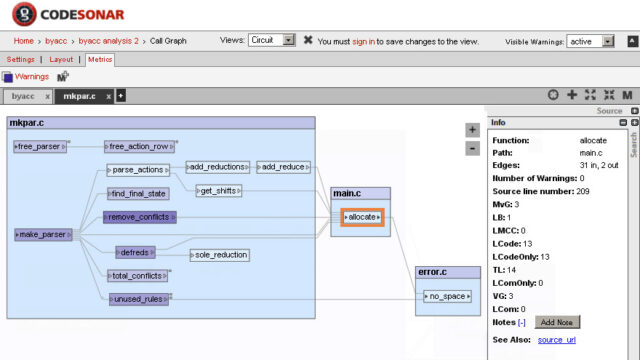
Static application security testing (SAST) tool for source and binary code
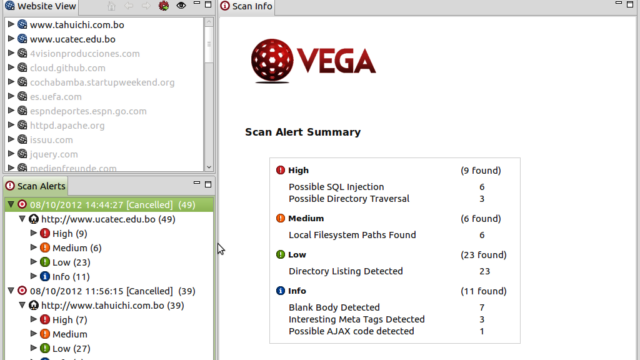
Open source web application security scanner
Link checker for local HTML files
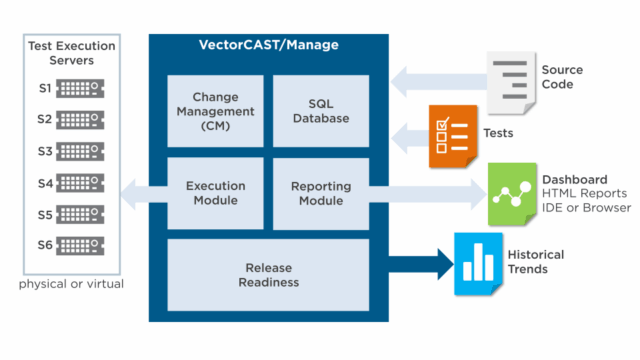
Unit, integration and coverage testing for embedded C, C++ and Ada
Application security testing and exposure management platform