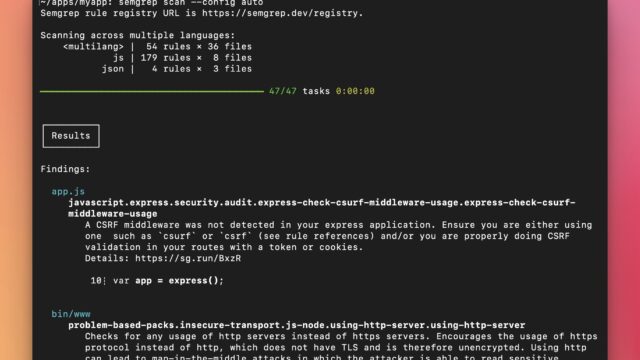
Semgrep
Fast static analysis with rules that look like code
Discover. Evaluate. Test.
Black-box web application vulnerability scanner
Wapiti is an open source web application vulnerability scanner. It performs black-box scans: it crawls the pages of a deployed application to find scripts and forms where data can be injected, then acts as a fuzzer, injecting payloads to check whether a script is vulnerable.
Detected issues include SQL, XPath and LDAP injections, reflected and stored cross-site scripting, file disclosure, command execution, XXE injection, server-side request forgery, cross-site request forgery, weak .htaccess configurations and backup copies of scripts. It also searches for dangerous files using the Nikto database, enumerates folders and files, detects uncommon HTTP methods, evaluates CSP, checks HTTP security headers and cookie flags, and can brute-force login forms.
Wapiti is written in Python 3 and distributed under the GPL-2.0; it is actively developed on GitHub, with version 3.3.2 released in August 2026.
There are no reviews yet.
Fast static analysis with rules that look like code
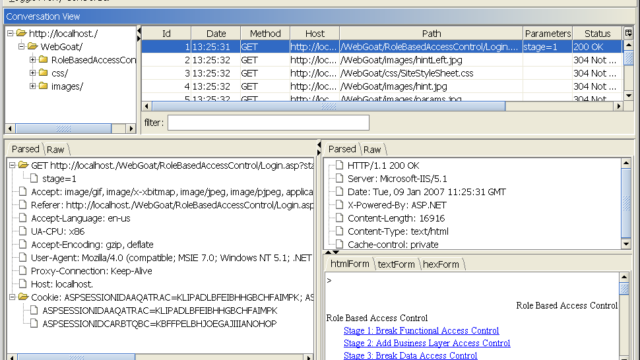
Framework for analysing HTTP(S) application traffic

Binary software composition analysis (formerly Protecode)
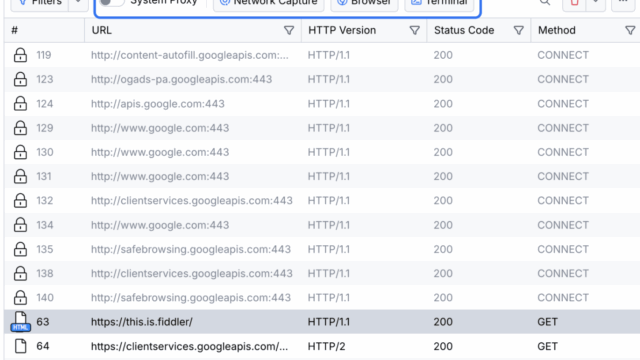
Web debugging proxy for capturing and inspecting HTTP(S) traffic

Static analysis security scanner for Ruby on Rails applications
Open source web server scanner