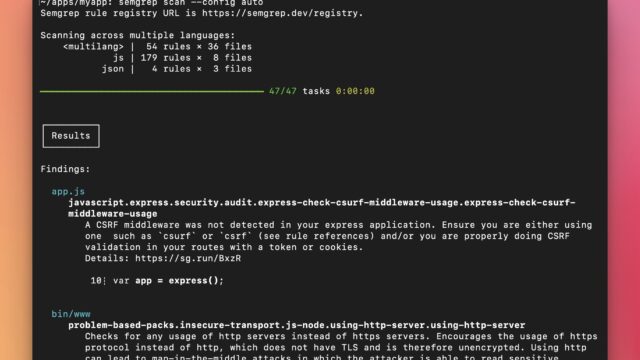
Semgrep
Fast static analysis with rules that look like code
Discover. Evaluate. Test.
Static analysis (SAST) tool for finding defects and vulnerabilities in source code
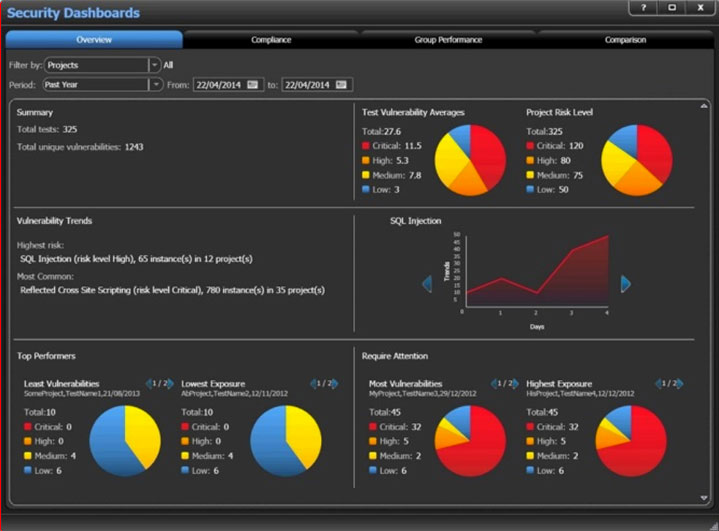
Coverity is a static application security testing (SAST) tool that analyses source code without executing it to find quality defects and security vulnerabilities, across 22 programming languages and more than 250 frameworks, with a particular focus on C and C++. It checks standards such as OWASP Top 10, CWE Top 25, CERT, MISRA and AUTOSAR, and is certified for safety use under ISO 26262 and DO-178C.
Coverity is published by Black Duck (formerly the Synopsys Software Integrity Group). It integrates with IDEs, code review and CI/CD, and is available on premises, including air-gapped deployments, or as SaaS through the Polaris platform. It is a commercial product.
There are no reviews yet.
Fast static analysis with rules that look like code
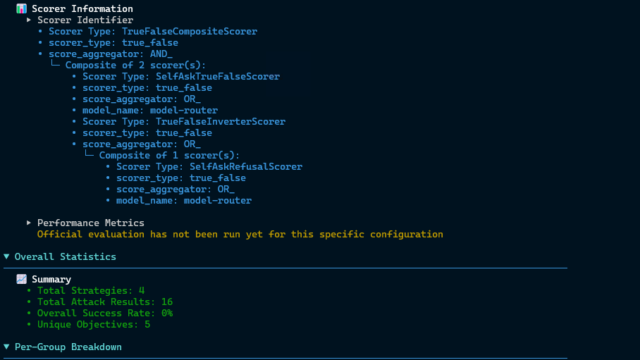
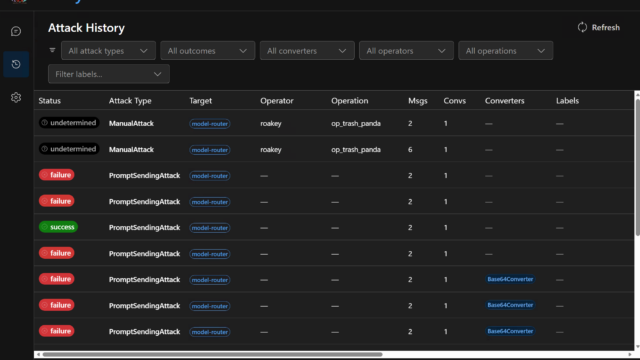
Python Risk Identification Tool for generative AI red teaming
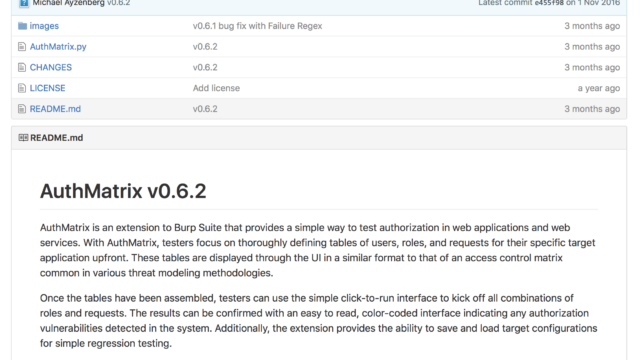
Burp Suite extension for testing authorization in web applications
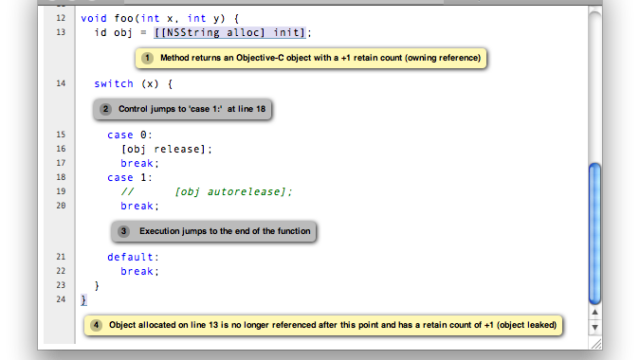
Source code analysis tool for C, C++ and Objective-C, part of Clang
Client-side HTML checker for WCAG and Section 508
Static analyzer for numerical precision in C and Ada programs